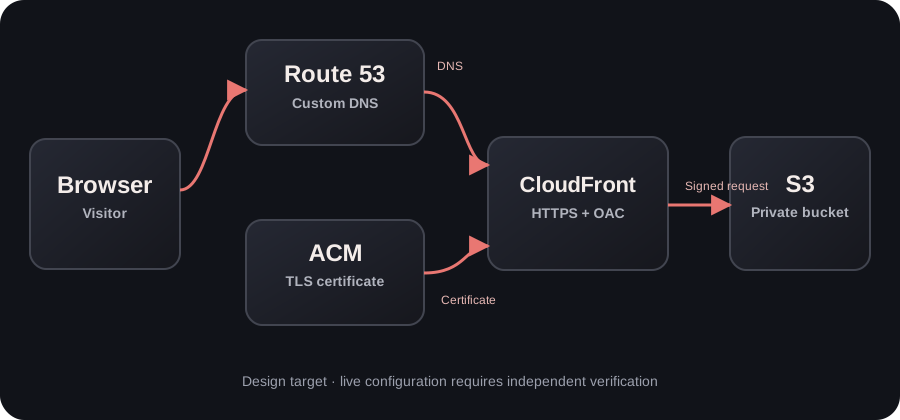
Architecture first
A private object store and a global content-delivery layer separate storage from public access.
A cloud engineering lab exploring how specialized AI agents can plan, build, secure, and validate a modern static website on AWS.
A thoughtful demonstration of cloud fundamentals, security boundaries, and agent-assisted engineering.
A private object store and a global content-delivery layer separate storage from public access.
Distinct roles exchange validated task objects and evidence instead of relying on copied prompts.
HTTP checks, configuration inspection, and reproducible test results make outcomes verifiable.
Visitors reach CloudFront over HTTPS. The S3 origin is private, with access limited to authorized CloudFront requests. The custom domain and certificate are configured when registration is complete.
See the complete architecture →